01 // SECURITY & DATA GOVERNANCE

Enterprise security and data governance for EHS, ESG, and Water compliance

Sophisticated security built for the most sensitive data

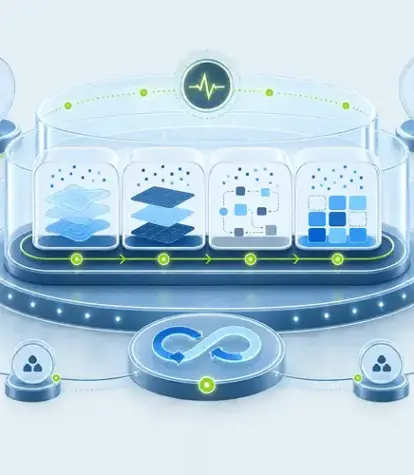
When a regulator asks your organization to defend a data point, the answer has to be immediate, complete, and unambiguous. Locus Platform is built to support that moment. We hold concurrent SOC 1 Type 2 and SOC 2 Type 2 certifications — independently verified and covering our own operations, not only our cloud host's. Your data is encrypted, access-controlled, audit-trailed, and recoverable from the moment it enters the platform.

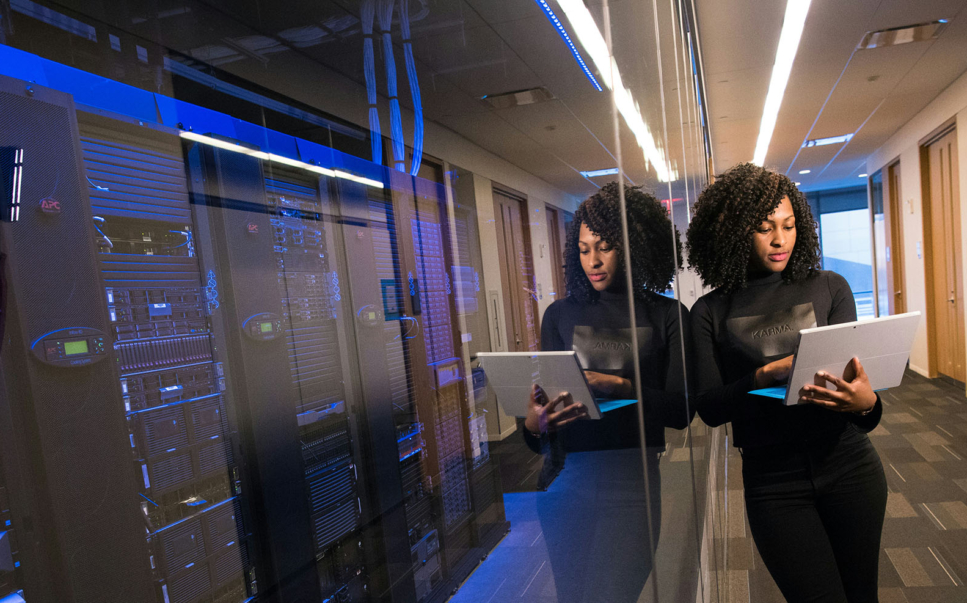
Professional working on laptop beside servers

02 // Third-Party Verified

The only EHS vendor with concurrent SOC 1 and SOC 2 Type 2 certifications

Locus is the only EHS software provider to hold both SOC 1 Type 2 and SOC 2 Type 2 certifications concurrently. More importantly, these certifications cover Locus's own financials, operations, and security controls — not merely the protocols of our hosting provider. Most enterprise software vendors point to their cloud host's security certifications and stop there. Locus's certifications are our own, independently audited, and updated as of June 2025.

SOC reports are available to qualified organizations under a non-disclosure agreement. Your Locus representative can initiate that process during your evaluation.

03 // Benefits

Sophisticated security protocols surround the entire Locus ecosystem.

  • Concurrent SOC 1 Type 2 and SOC 2 Type 2
  • 99.99%+ verified uptime continuously since 2014
  • All data encrypted at rest and in transit
  • Role-based access controls down to the field and workflow level
  • Multi-factor authentication for all remote access
  • Mobile - Managing Drinking Water Quality Data and Compliance
  • Immutable audit trails for every action and data event
  • Single sign-on support via OAuth 2.0
  • Annual independent penetration testing and vulnerability scanning
  • Fully managed AWS hosting in US data centers
  • SOC reports available under NDA for vendor evaluation

Security that works across every program, every user, every site

04 // Enterprise-Grade

Access Control and Identity Management

Every Locus software user accesses only the data and functions their role permits. Access is controlled at the facility, data field, and workflow approval level; administrators define role hierarchies without writing code, and changes take effect immediately. Multi-factor authentication is required for all remote and VPN access. Locus supports single sign-on via OAuth 2.0, allowing enterprise customers to manage Locus access through their existing identity provider. Access is granted during onboarding and revoked at termination, with dormant accounts disabled automatically.

Explore No-Code Configuration →
Data Encryption

All customer data stored in Locus Platform is encrypted at rest using industry-standard encryption with FIPS-validated cryptographic modules. All data transmitted between users and the platform is encrypted in transit using current TLS standards. Documents and attachments are stored in encrypted cloud storage. Data backups are encrypted before replication and stored offsite. These protections apply consistently across every Locus customer, every facility, and every data type — they are not options that can be enabled or disabled.

Industry specific environmental data management & EHS software applications

Immutable Audit Trails

Every action within Locus Platform generates a timestamped, tamper-evident log entry: data entries, form submissions, workflow transitions, report generation, access events, and administrative changes. These logs are centralized, maintained for regulatory review, and accessible to authorized administrators. For organizations in regulated industries where proving data integrity to an auditor or regulator is a legal requirement, the Locus audit trail provides the traceability that makes that proof possible without reconstructing records from email or spreadsheets.

Explore Data Quality & Validation →

Infrastructure and Availability

Locus Platform is hosted exclusively on Amazon Web Services within US-based data centers. The AWS environment provides redundant infrastructure, automated failover, and continuous security monitoring that underpins the availability your compliance programs depend on. Locus's own network security — firewalls, intrusion prevention, and network segmentation — operates in parallel with AWS infrastructure controls. Locus has maintained greater than 99.99% verified uptime continuously since 2020, published through a third-party uptime monitoring service.

SaaS for Better Environmental Stewerdship

Backup, Recovery, and Business Continuity

Locus Technologies implements automated, encrypted backups with offsite replication and regularly tested restoration procedures. The platform's disaster recovery plan is formally documented and tested annually. Specific recovery time and recovery point objectives are documented in Locus's security data sheet, available to organizations in active vendor evaluation. Locus has maintained greater than 99.99% uptime since 2020.

Tertiary Backup Architecture

Ransomware and AI-driven attacks have changed what backup and recovery must mean. Sophisticated attacks no longer stop at live systems. They target backup repositories, replication environments, and disaster recovery infrastructure specifically to eliminate the recovery path. A backup strategy that assumes the attacker hasn't reached the backup layer is no longer sufficient. Locus's tertiary backup architecture provides a third tier of data protection beyond production systems and standard backups. Even if a primary environment is compromised and conventional backups are affected, a protected recovery path for your compliance data remains intact, keeping your regulatory record accessible and defensible when it matters most. This protection is built into Locus Platform's multitenant SaaS architecture, which also means security investments, patches, and resilience improvements deploy consistently across all customers.

Governance, Privacy, and Vendor Oversight

Locus complies with applicable global privacy laws and maintains documented data governance policies covering collection, use, retention, and disposal. All Locus employees and contractors sign confidentiality agreements and undergo background checks. Third-party vendors, including cloud infrastructure providers, are subject to annual risk assessments. For organizations requiring documentation of vendor controls, Locus's security data sheet and SOC reports provide the detail that procurement and IT teams need to complete their evaluation.

05 // Trust

Locus Technologies is proven and battle-tested

Organizations in nuclear, federal, utility, and industrial sectors trust Locus with their most consequential environmental data — program areas where data integrity is not a preference but a legal and regulatory requirement.

Trusted by:

06 // Key Takeaways

The enterprise foundation behind every Locus solution

  1. Concurrent SOC 1 Type 2 and SOC 2 Type 2 certifications, independently audited
  2. Security architecture aligned with NIST, CIS, and ISO 27001 frameworks
  3. All data encrypted at rest and in transit using FIPS-validated modules
  4. Role-based access control at facility, field, and workflow level
  5. Multi-factor authentication for all remote and VPN access
  6. Single sign-on via OAuth 2.0
  7. Immutable, centralized audit trails with automated alerting
  8. Annual independent penetration testing and vulnerability scanning
  9. Fully managed AWS hosting in US data centers with 99.99%+ uptime
  10. Documented backup, recovery, and business continuity procedures
  11. SOC reports available under NDA for qualified vendor evaluations

08 // Software Demonstration

Ready to dig into the details?

Our security data sheet covers encryption standards, recovery objectives, and network architecture. SOC reports are available under NDA.
Book a demo

Frequently Asked Questions

09 // FAQ

Locus holds concurrent SOC 1 Type 2 and SOC 2 Type 2 certifications, independently verified by a third-party auditor. These cover Locus's own financial controls, operational processes, and security protocols — not only those of our cloud hosting provider. Reports were last updated June 2025 and are available to qualified organizations under a non-disclosure agreement. Contact your Locus representative to request access during your evaluation.

All customer data in Locus software is encrypted at rest using industry-standard encryption with FIPS-validated cryptographic modules and encrypted in transit using current TLS standards. Documents and attachments are stored in encrypted cloud storage. Backups are encrypted before replication and stored offsite. These protections apply across every customer and every data type; they are not optional configurations.

Locus provides role-based access control at the facility, data field, and workflow approval level. Administrators define role hierarchies without writing code, changes take effect immediately, and access is revoked automatically at termination. Multi-factor authentication is required for all remote access. Locus supports single sign-on via OAuth 2.0, allowing organizations to manage Locus access through their existing identity provider without maintaining a parallel credential set.

Locus Platform is hosted exclusively on Amazon Web Services within US-based data centers. The AWS environment provides redundant infrastructure, automated failover, and continuous security monitoring. Locus's own network security operates in parallel with AWS infrastructure controls. Locus has maintained greater than 99.99% verified uptime continuously since 2020, published through a third-party uptime monitoring service accessible to any prospective customer.

Locus provides a security data sheet covering encryption standards, recovery objectives, network architecture, access control specifics, and vendor risk management protocols. The information is available to organizations in active evaluation. SOC 1 Type 2 and SOC 2 Type 2 reports are available under NDA. Security questionnaires submitted by procurement or IT teams are handled by Locus's technical team with response times aligned to your evaluation timeline. Contact your Locus representative to initiate.

Every action within Locus Platform generates an immutable, timestamped audit trail — data entries, form submissions, workflow transitions, report generation, and administrative events. These logs are maintained for regulatory review and are accessible to authorized administrators within the platform. When a regulator questions a data point, Locus customers can trace it back through its full history without reconstructing records from email, spreadsheets, or paper files.